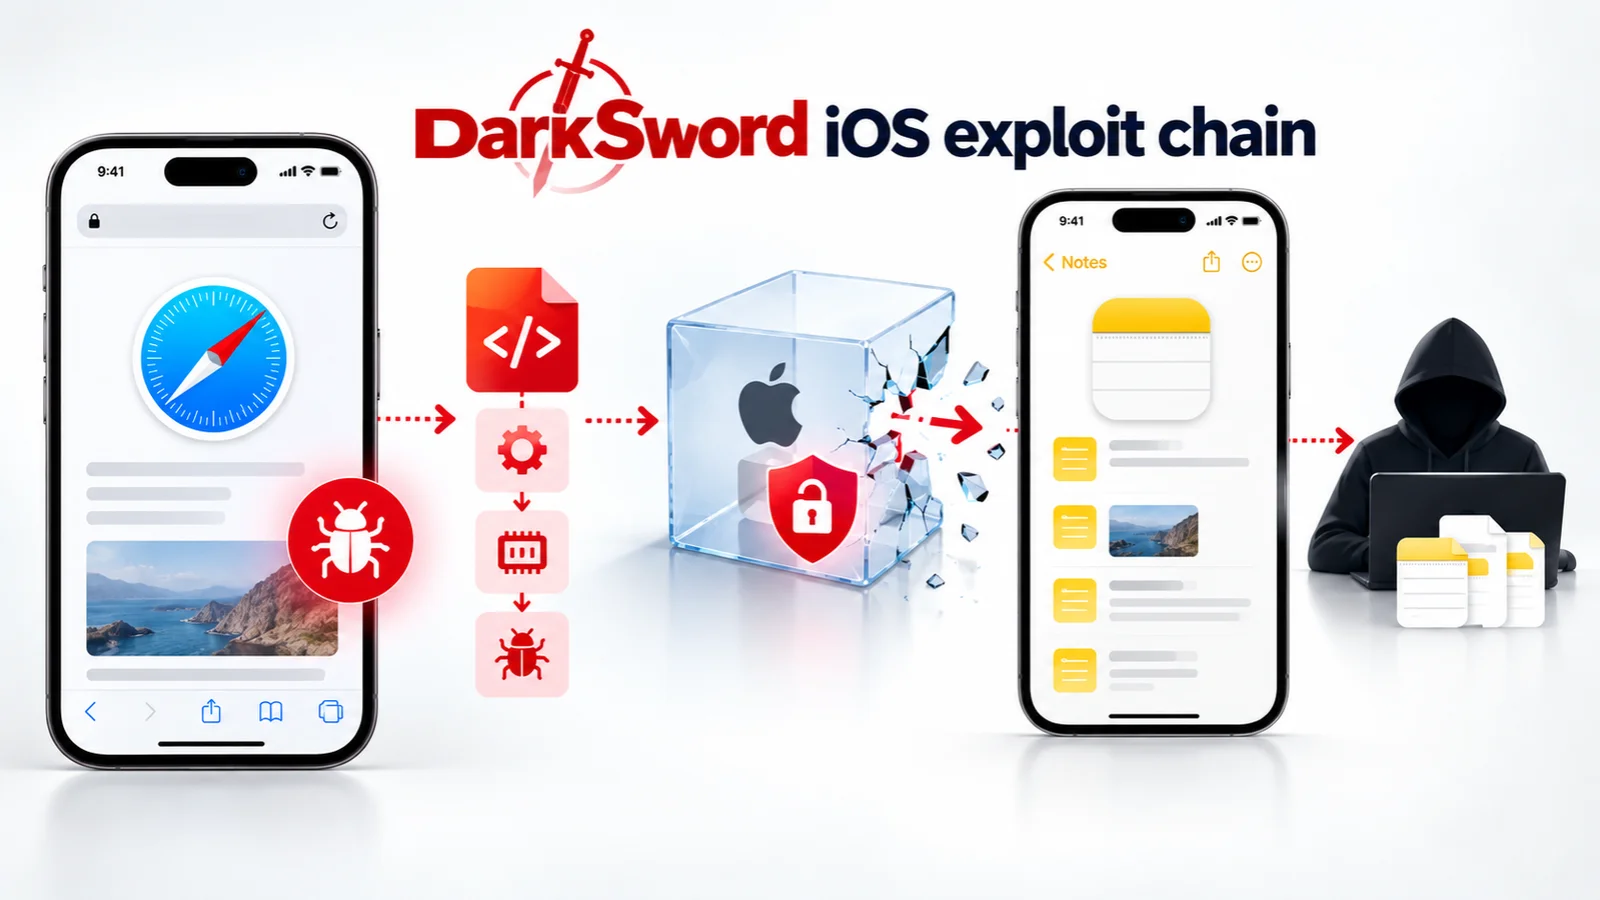
Zimperium zLabs Coruna iOS eksploit kampaniyasi endi jabrlanuvchining iOS versiyasiga qarab tanlanadigan ikkita iOS eksploit zanjirini tarqatishini aniqladi. DarkSword'dan olingan zanjir yangi iPhone'larda Safari sandboxini chetlab o'tadi va Apple Notes ma'lumotlarini o'g'irlagan.
Instagram reklamalari va tashlab ketilgan teglar orqali tarqalayotgan Coruna va DarkSword haqidagi so'nggi xabarlar bu to'plamlar hali ham tarqalayotganini ko'rsatadi.
Zimperium tomonidan chop etilgan texnik tadqiqotga ko'ra, iOS 17.2.1 yoki undan oldingi versiyadagi qurilmalar eski Coruna framework'ini oladi. Keyingi tuzilmalar DarkSword'dan olingan zanjirni oladi.
2026-yil oktyabr oyigacha zLabs Coruna oilasi kodini tarqatadigan 608 domenni sanadi. 93 ta saytdan olingan konfiguratsiyalar 21 ta kuzatuv kollektoriga mos keladi.
Aldovlar orasida tanishuv portallari, AI-hamroh ilovalari, kripto aksiyalari va striming saytlari bor. Ba'zilari buzilgan qonuniy saytlar bo'lib, ular to'plamni yashirin iframe'lar orqali yuklaydi.
Google Threat Intelligence Group Coruna'ni birinchi marta 2026-yil mart oyida hujjatlashtirgan. U iOS 13.0 dan 17.2.1 gacha bo'lgan beshta eksploit zanjiri va 23 ta eksploitni tasvirlaydi.
.webp)
Exploit Aldov Interfeysi Variantlari (Rasm manbasi: Zimperium)
Jabrlanuvchi hech qanday ilova o'rnatmaydi va hech qanday so'rovni qabul qilmaydi. Dekoy sahifa odatdagidek ko'rsatiladi, yashirin iframe esa eksploitni yuklaydi. Ba'zi aldovlar TikTok foydalanuvchilariga havolani Safari'da ochishni aytadi, bu esa loader'ga kerak bo'lgan muhitdir.
SafeDep Coruna kodining buzilgan npm paketi art-template versiyalarida mos kelishini topdi. Shunday qilib, sayt o'zining bog'liqlik daraxti orqali to'plamni tarqatishi mumkin, blok ro'yxatlari uchun hech qanday aldov domeni bo'lmaydi. SafeDep yozuvi tahlil qilingan infratuzilma o'shandan beri oflayn bo'lganini qayd etadi.
zLabs iOS 18 zanjirini melatibiru[.]win orqali tahlil qildi, u o'n ta eksploit skriptini ssc[.]vever3eds[.]com staging hostidan tortib oldi. iOS 18.6.2 da loader rceworker18.6.js ni Web Worker'da ishga tushiradi.
Zanjir keyin bir nechta imtiyoz chegaralarini kesib o'tadi, imtiyozsiz WebContent jarayonida masofaviy kod bajarilishini, WebKit GPU jarayoni (sbx0) orqali sandbox chetlab o'tilishini, mediaplaybackd ga o'tishni, media daemon (sbx1) va keyingi payload bosqichlarini boshqaradigan post-escape worker'ni amalga oshiradi.
zLabs GPU jarayoni va mediaplaybackd ikkalasi ham /private/var/tmp/c2ipc ni yaratishga urinishini ko'rdi va sandbox ikkalasini ham blokladi. mediaplaybackd keyin peworker.js da sozlangan C2 serveri ccsigen321qc[.]com ga TLS ClientHello yubordi.
.webp)
Coruna Kampaniyasi Oshkor Qilish Xronologiyasi (Rasm manbasi: Zimperium)
Qurilma C2 dan yana yettita JavaScript modulini, jumladan c2agent.js va telegramv1.js ni yuklab oldi. Telegram moduli mahalliy saqlashni tahlil qilish va autentifikatsiya materialini ajratib olish uchun qurilgan. zLabs C2 ga 144 ta HTTPS POST so'rovini qayd etdi, barchasi HTTP 200 bilan javob berildi.
Qurilma Apple Notes ma'lumotlar bazasini (NoteStore.sqlite) va 214 ta o'rnatilgan ilova inventarini yukladi. Bu ulanishni SpringBoard jarayoni boshladi.
Coruna zanjirining native modullari ChaCha20 shifrlash va sertifikat tekshiruvi o'chirilgan HTTPS dan foydalanadi. Ular shuningdek Apple Mobile File Integrity (AMFI) holatini manipulyatsiya qiladi va crash loglari hamda Safari veb-sayt ma'lumotlarini o'chiradi. 19 ta konteyner bo'yicha tadqiqotchilar 24 ta alohida binar faylni, ulardan o'n ikkitasi versiyaga xos kernel modul tuzilmalari bo'lganini ajratib oldi.
Umumiy artefaktlar infratuzilmani birlashtiradi. Bular 29,924 baytli runtime, globalThis.obChTK nom maydoni va loader identifikatori cecd08aa6ff548c2 ni o'z ichiga oladi.
Zanjirdagi har bir CVE allaqachon tuzatilgan, shuning uchun iOS ni yangilash asosiy himoya hisoblanadi. Yuqori xavfli foydalanuvchilar Lockdown Mode ni yoqishlari kerak.
Xavfsizlik jamoalari OS versiya siyosatlarini joriy etishi, BYOD qurilmalarini qamrab olishi, mobil tahdid himoyasini joylashtirishi va zararli dastur ularni o'chirishidan oldin diagnostika loglarini to'plashi kerak. To'liq indikatorlar Zimperium IOC omborida.
Zimperium zLabs has found that the Coruna iOS exploit campaign now serves two iOS exploit chains, picked by the victim’s iOS version. A DarkSword-derived chain escapes Safari’s sandbox on newer iPhones and has stolen Apple Notes data.
Recent coverage of Coruna and DarkSword spreading through Instagram ads and abandoned tags shows the kits are still spreading.
According to technical research published by Zimperium, devices on iOS 17.2.1 or earlier receive the legacy Coruna framework. Later builds receive the DarkSword-derived chain.
Through October 2026, zLabs counted 608 domains delivering Coruna-family code. Configurations from 93 of those sites map to 21 tracking collectors.
The lures include dating portals, AI-companion apps, crypto promotions and streaming sites. Some are compromised legitimate sites that load the kit through hidden iframes.
Google’s Threat Intelligence Group first documented Coruna in March 2026. It describes five exploit chains and 23 exploits covering iOS 13.0 through 17.2.1.
.webp)
Exploit Lure Interface Variants (Image Source: Zimperium)
The victim installs no app and accepts no prompt. A decoy page renders normally while a hidden iframe loads the exploit. Some lures tell TikTok users to open the link in Safari, which is the environment the loader needs.
SafeDep found matching Coruna code in compromised versions of the npm package art-template. A site can therefore serve the kit through its own dependency tree, with no lure domain for blocklists to catch. The SafeDep write-up notes that the infrastructure it analyzed has since gone offline.
zLabs analyzed the iOS 18 chain through melatibiru[.]win, which pulled ten exploit scripts from the staging host ssc[.]vever3eds[.]com. On iOS 18.6.2, the loader runs rceworker18.6.js in a Web Worker.
The chain then crosses several privilege boundaries, achieving remote code execution in the unprivileged WebContent process, a sandbox escape through WebKit’s GPU process (sbx0), a pivot into mediaplaybackd, the media daemon (sbx1), and a post-escape worker that manages later payload stages.
zLabs saw both the GPU process and mediaplaybackd try to create /private/var/tmp/c2ipc, and the sandbox blocked both attempts. mediaplaybackd then sent a TLS ClientHello to ccsigen321qc[.]com, the C2 server configured in peworker.js.
.webp)
Coruna Campaign Disclosure Timeline (Image Source: Zimperium)
The device fetched seven more JavaScript modules from the C2, including c2agent.js and telegramv1.js. The Telegram module is built to parse local storage and extract authentication material. zLabs recorded 144 HTTPS POST requests to the C2, all answered with HTTP 200.
The device uploaded the Apple Notes database (NoteStore.sqlite) and an inventory of 214 installed apps. The SpringBoard process initiated that connection.
The Coruna chain’s native modules use ChaCha20 encryption and HTTPS with certificate validation disabled. They also manipulate Apple Mobile File Integrity (AMFI) state and delete crash logs and Safari website data. Across 19 containers, researchers extracted 24 distinct binaries, twelve of which are version-specific kernel module builds.
Shared artifacts tie the infrastructure together. These include the 29,924-byte runtime, the globalThis.obChTK namespace and the loader identifier cecd08aa6ff548c2.
Every CVE in the chain is already patched, so updating iOS is the main defense. High-risk users should enable Lockdown Mode.
Security teams should enforce OS version policies, include BYOD devices, deploy mobile threat defense and collect diagnostic logs before the malware deletes them. The full indicators are in Zimperium’s IOC repository.