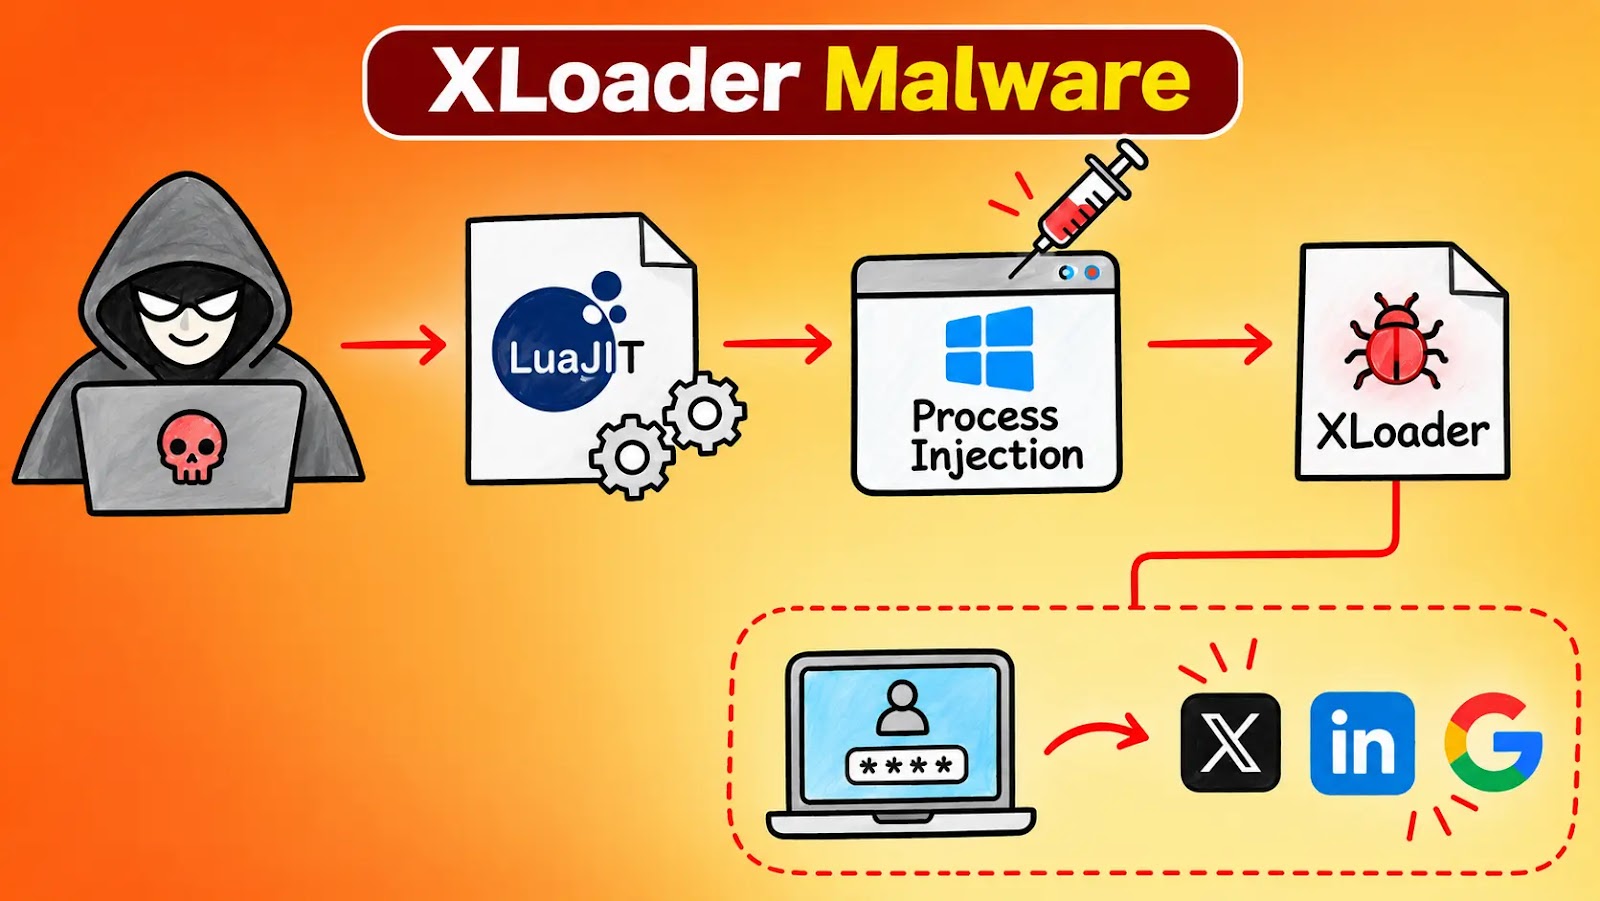
Yangi XLoader zararlanish zanjiri. U ma'lumot o'g'irlovchini o'rnatilgan LuaJIT interpretatori ichida yashiradi. U uni umumiy bo'lim in'ektsiyasi orqali boshqa Windows jarayoniga ko'chiradi. Kampaniya biznes mavzusidagi elektron pochta aldovlaridan foydalanadi. U shuningdek Agent Tesla, Remcos va XWorm ni ham tarqatdi. Zanjir buyurtma va to'lov elektron pochta xabarlari bilan boshlanadi. Bir yunon tilidagi xabar mavzusi […] bilan boshlanadi.
A new XLoader infection chain. It hides the credential stealer inside an embedded LuaJIT interpreter. It moves it into another Windows process through shared-section injection. The campaign uses business-themed email lures. It also delivered Agent Tesla, Remcos and XWorm . The chain starts with order and payment emails. One Greek-language message has a subject starting […] The post Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.