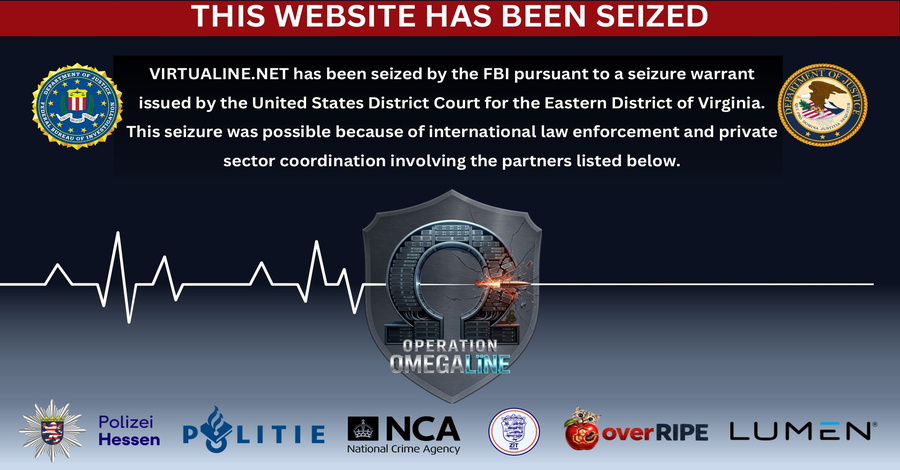
AQSh Adliya vazirligi (DoJ) seshanba kuni Virtualine nomli o'q o'tkazmaydigan xosting provayderi (BPH) bilan bog'liq domen musodara qilinganini e'lon qildi.
Bu harakat xizmatning "voyaga yetmaganlarning jinsiy mazmundagi tasvirlarini reklama qilish, kattalar va voyaga yetmaganlarning roziligisiz intim vizual tasvirlarini qasddan oshkor qilish va jinoiy xatti-harakatni yashirish va targ'ib qilishga mo'ljallangan xalqaro pul yuvish" kabi keng tarqalgan jinoiy faoliyatni amalga oshirish va osonlashtirish uchun ishlatilganiga javoban amalga oshirildi, deb aytdi DoJ.
"virtualine[.]net" domeniga tashrif buyurganlar endi uning AQSh Federal Tergov Byurosi (FBI) tomonidan xalqaro huquqni muhofaza qiluvchi organlar va xususiy sektor subyektlari, jumladan Gessen shtati politsiyasi, Niderlandiya Milliy Politsiya Korpusi, Buyuk Britaniya Milliy Jinoyatchilik Agentligi, OverRIPE va Lumen Technologies bilan hamkorlikda o'tkazilgan muvofiqlashtirilgan operatsiya doirasida musodara qilinganini bildiruvchi xabar bilan kutib olinadi.
Sud hujjatlariga ko'ra, Virtualine — shuningdek Secury, Massgod, Spamhouse, Lanedo va Omegatech nomlari bilan ham faoliyat yuritgan — o'z xizmatlarini kiberjinoyatchilik forumlarida reklama qilib, ularni fishing, karting, elektron pochta spam va port skanerlash uchun ishlatish mumkinligini da'vo qilgan, bolalar mazmuni va terrorchilik faoliyati bundan mustasno.
2025-yil iyun oyida HackForums'da provayder "Virtualine sizning oxirgi uchta terapevtingizdan ko'proq shikoyatni e'tiborsiz qoldirdi" deb maqtangan. Joriy yilning mart oyida u shuningdek "qo'shimcha himoya rejasi"ni marketing qila boshladi, bu rejada mijozlarga rasmiy so'rovlar kelganda ularning jinoiy infratuzilmasini Virtualine bilan bog'liq bo'lmagan soxta kompaniyaga ko'chirish va'da qilingan.
Internet Archive tomonidan saqlangan suratlar standart rejalar oyiga $19,99 dan (1 virtual CPU, 2 GB xotira va 30 GB saqlash) $179,99 gacha (24 vCPU, 64 GB xotira va 130 GB xotira) turishini ko'rsatadi. Virtualine shuningdek CPU, xotira va saqlash bo'yicha optimallashtirilgan rejalarni oyiga $21,99 dan $379,99 gacha taklif qilgan.
"O'z serverida 'bolalar mazmuni'ga ruxsat bermasligini reklama qilganiga qaramay, Virtualine sud yozuvlarida Vendor 1 deb aniqlangan veb-saytni ongli ravishda xost qildi," deb aytdi DoJ. "Vendor 1 — foydalanuvchilarga voyaga yetmaganlar va kattalarning yalang'och, jinsiy mazmundagi va/yoki jinsiy ochiq tasvirlari va videolarini joylashtirish va sotish imkonini beradigan jinoiy onlayn forum."
"Vendor 1 shuningdek foydalanuvchilar xakerlarga jabrlanuvchilarning onlayn hisoblariga roziligisiz kirish va ochiq tasvirlar va videolarni noqonuniy olish uchun to'lashlari mumkin bo'lgan xaker-xizmatini targ'ib qiladi. 2026-yil yanvar oyida, Virtualine Vendor 1 ga IP manzil tayinlaganidan taxminan bir oy o'tib, Virtualine ushbu serverdagi voyaga yetmaganlarning jinsiy ochiq tasvirlari va videolari haqida xabarlar olishni boshladi."
Adliya vazirligi Virtualine Germaniya, Kanada va Avstraliyadagi huquqni muhofaza qiluvchi organlardan; AQShdagi Yo'qolgan va Ekspluatatsiya Qilingan Bolalar Milliy Markazidan (NCMEC); va jabrlanuvchining advokatidan ko'plab xabarlar olganiga qaramay, Vendor 1 xizmatlarini xost qilishni davom ettirganini aytdi.
Virtualine shuningdek Vendor 1 bilan yaqindan hamkorlik qilib, mijozlari noqonuniy mazmunni yuklab olishlari va sotib olishni tugatgandan so'ng yuklab olishlari mumkin bo'lgan yangi veb-sayt yaratgan. Vazirlik qo'shimcha qilganidek, ushbu veb-sayt hozirgacha Virtualine tomonidan xost qilinmoqda.
"Virtualine.net Virtualine mijozlari, jumladan Vendor 1 uchun bir qator to'lov variantlarini o'z ichiga olgan," deb aytdi DoJ. "Virtualine BTC [NO-AML], mijozlarga o'z mablag'lari noqonuniy deb belgilanishidan xavotirlanmasdan to'g'ridan-to'g'ri to'lash imkonini beradigan maxsus xostlanmagan bitcoin manzillari orqali to'lovni qabul qilgan."
"Virtualine jinoiy mijozlari Virtualinega to'lagan mablag'lar, ularning ba'zilari turli jinoiy guruhlarga to'g'ridan-to'g'ri kuzatilishi mumkin, Virtualine tomonidan qabul qilingan va keyin mablag'lar manbasini yashirish uchun yanada yuvilgan."
Blockchain razvedka firmasi Chainalysis o'z tahlilida Virtualine xostlanmagan hamyon manzillari orqali to'g'ridan-to'g'ri Bitcoin to'lovlarini qabul qilganini, bu jinoiy mijozlarga xostlangan birjalarda muvofiqlik tekshiruvlarini ishga tushirmasdan to'lash imkonini berganini aytdi.
"Virtualine'ning zanjirdagi izi kiberjinoyatchilik ekotizimining keng kesimiga, jumladan ransomware operatorlari, infostealer infratuzilmasi, rus tilidagi kiberjinoyatchilik forumlari, noqonuniy do'konlar va firibgarlik va fishing manzillariga to'g'ridan-to'g'ri ta'sir qiladi," deb aytdi u.
Sayt musodara qilinganidan so'ng, Virtualine operatori ochiq xat e'lon qilib, xizmat bolalar jinsiy zo'ravonlik materialini (CSAM) ongli ravishda xost qilganligi haqidagi ayblovlarni rad etdi. Operator shuningdek CSAM bo'yicha hamkorlik so'rovlariga 24 soat ichida chora ko'rganini da'vo qildi. Ular Telegram kanalida e'lon qilingan postda mijoz ma'lumotlari xavfsiz ekanligini ta'kidladi.
"Biz 'Vendor 1' deb ta'riflangan mijoz bilan bog'liq taqiqlangan materialni aniqlaganimizda, biz ushbu mijoz bilan munosabatimizni tugatdik," deb qo'shimcha qildi shaxs, "Virtualine besh yildan beri mening hayotimning bir qismi bo'lib kelgan" deb da'vo qilib.
"Iltimos, bitta mijozning harakatlari tufayli menga va Virtualinega ishonch bildirgan o'n minglab mijozlarga shubha bilan qaramang. Men 'Vendor 1' bo'yicha so'rovlaringizga javob berishga tayyor ekanligimni bilishingizni xohlayman."
2025-yil sentyabr oyida Spamhaus Project Virtualine o'z faoliyatini AS209800 ga kengaytirganini ma'lum qildi. "Mijoz tekshiruvi zaif bo'lgan Turkiya va AQShda joylashgan IP manzil brokerlari tufayli Virtualine internet suiiste'molini ta'minlash uchun yangi IPv4 prefikslarini olishni davom ettirmoqda. AS209800 hozirda aurologic GmbH, bir nechta boshqa o'q o'tkazmaydigan xosting operatsiyalarini tarqatadigan xosting provayderi orqali yo'naltirilmoqda."
"Yo'qotilgan ASN o'z-o'zidan BPH to'xtaganini anglatmaydi," deb aytdi Silent Push. "Yangi ASN olish tezligi muammoning muhim qismidir va biz ASN ro'yxatdan o'tkazish jarayoni qattiqroq bo'lishi kerak deb hisoblaymiz."
The U.S. Department of Justice (DoJ) on Tuesday announced the seizure of a domain associated with a bulletproof hosting provider (BPH) named Virtualine.
The move was in response to the service being used to commit and facilitate prolific criminal activity, including "the advertisement of sexually explicit images of minors, the intentional disclosure of nonconsensual intimate visual depictions of adults and minors, and international money laundering designed to conceal and promote criminal conduct," the DoJ said.
Visitors to the "virtualine[.]net" domain are now greeted by a message that states it has been seized by the U.S. Federal Bureau of Investigation as part of a coordinated operation between international law enforcement agencies and private sector entities, including the Hessen State Police, the National Police Corps of the Netherlands, the U.K. National Crime Agency, OverRIPE, and Lumen Technologies.
According to court documents, Virtualine, which also operated as Secury, Massgod, Spamhouse, Lanedo, and Omegatech, advertised its services to criminals on cybercrime forums, claiming that they can be used for phishing, carding, email spam, and port scanning, with the exception of child content and terrorism activities.
In June 2025 on HackForums, the provider is alleged to have boasted that "Virtualine ignored more abuse than your last three therapists." Earlier this March, it also began marketing an "additional protection plan" that promised its customers to move their criminal infrastructure to a shell company unaffiliated with Virtualine when receiving official requests from law enforcement agencies.
Snapshots captured by the Internet Archive show that standard plans cost anywhere between $19.99 per month for one virtual CPU, 2GB memory, and 30 GB storage to $179.99 per month for 24 vCPUs, 64 GB memory, and 130 GB memory. Virtualine also offered plans optimized by CPU, memory, and storage, starting from $21.99 per month to $379.99 per month.
"Despite advertising that it does not allow 'child contents' on its server, Virtualine knowingly hosted a website that did so, identified in court records as Vendor 1," DoJ said. "Vendor 1 is a criminal online forum that allows users to post and sell access to nude, sexually suggestive, and/or sexually explicit images and videos of minors and adults."
"Vendor 1 also promotes a hack-for-hire service in which users can pay hackers to access victims’ online accounts without their consent and illicitly obtain explicit images and videos. In January 2026, about one month after Virtualine assigned an IP address to Vendor 1, Virtualine began receiving notifications about sexually explicit images and videos of minors on that server."
The Justice Department said Virtualine continued to host Vendor 1's services despite receiving numerous notices from law enforcement in Germany, Canada, and Australia; the National Center for Missing and Exploited Children (NCMEC) in the United States; and a victim's attorney.
Virtualine has also been accused of working closely with Vendor 1 to create a new website where its clients could upload their illicit content and download it upon completing a purchase. The website continues to be hosted by Virtualine to this day, the department added.
"Virtualine.net included a number of payment options for Virtualine's customers, including Vendor 1," the DoJ said. "Virtualine accepted payment through BTC [NO-AML], specific unhosted bitcoin addresses that allowed customers to direct pay without concern their funds would be flagged as illicit."
"The funds Virtualine's criminal customers paid to Virtualine, some of which can be traced directly to various criminal groups, were received by Virtualine and then further laundered to conceal the origin of the funds."
Blockchain intelligence firm Chainalysis, in its own analysis, said Virtualine accepted direct Bitcoin payments through unhosted wallet addresses, allowing criminal customers to pay without triggering compliance checks at hosted exchanges.
"Virtualine's on-chain footprint has direct exposure to a broad cross-section of the cybercrime ecosystem, including ransomware operators, infostealer infrastructure, Russian-language cybercrime forums, illicit shops, and scam and phishing addresses," it said.
Following the site seizure, the operator of Virtualine has published an open letter, refuting allegations that the service knowingly hosted child sexual abuse material (CSAM). The operator also claimed they have taken action on requests for cooperation concerning CSAM within 24 hours. In a post shared on their Telegram channel, they insisted that customer data was safe.
"When we identified prohibited material associated with the customer described as 'Vendor 1,' we ended our relationship with that customer," the individual added, claiming "Virtualine has been part of my life for five years."
"Please do not cast suspicion on me and the tens of thousands of customers who have trusted Virtualine because of the actions attributed to a single customer. I want you to know that I am prepared to respond to your requests concerning 'Vendor 1.'"
In September 2025, the Spamhaus Project revealed that Virtualine had expanded their operations to AS209800. "Thanks to Turkey- and U.S.-based IP address brokers with poor customer vetting procedures, Virtualine keeps obtaining new IPv4 prefixes for enabling internet abuse. AS209800 is currently routed via aurologic GmbH, a hosting provider proliferating several other bulletproof hosting operations."
"A lost ASN does not by itself mean the BPH has stopped," Silent Push said. "The speed of acquiring a new ASN is a crucial part of the problem, and we believe the process for registering an ASN should be tougher."
Found this article interesting? Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.