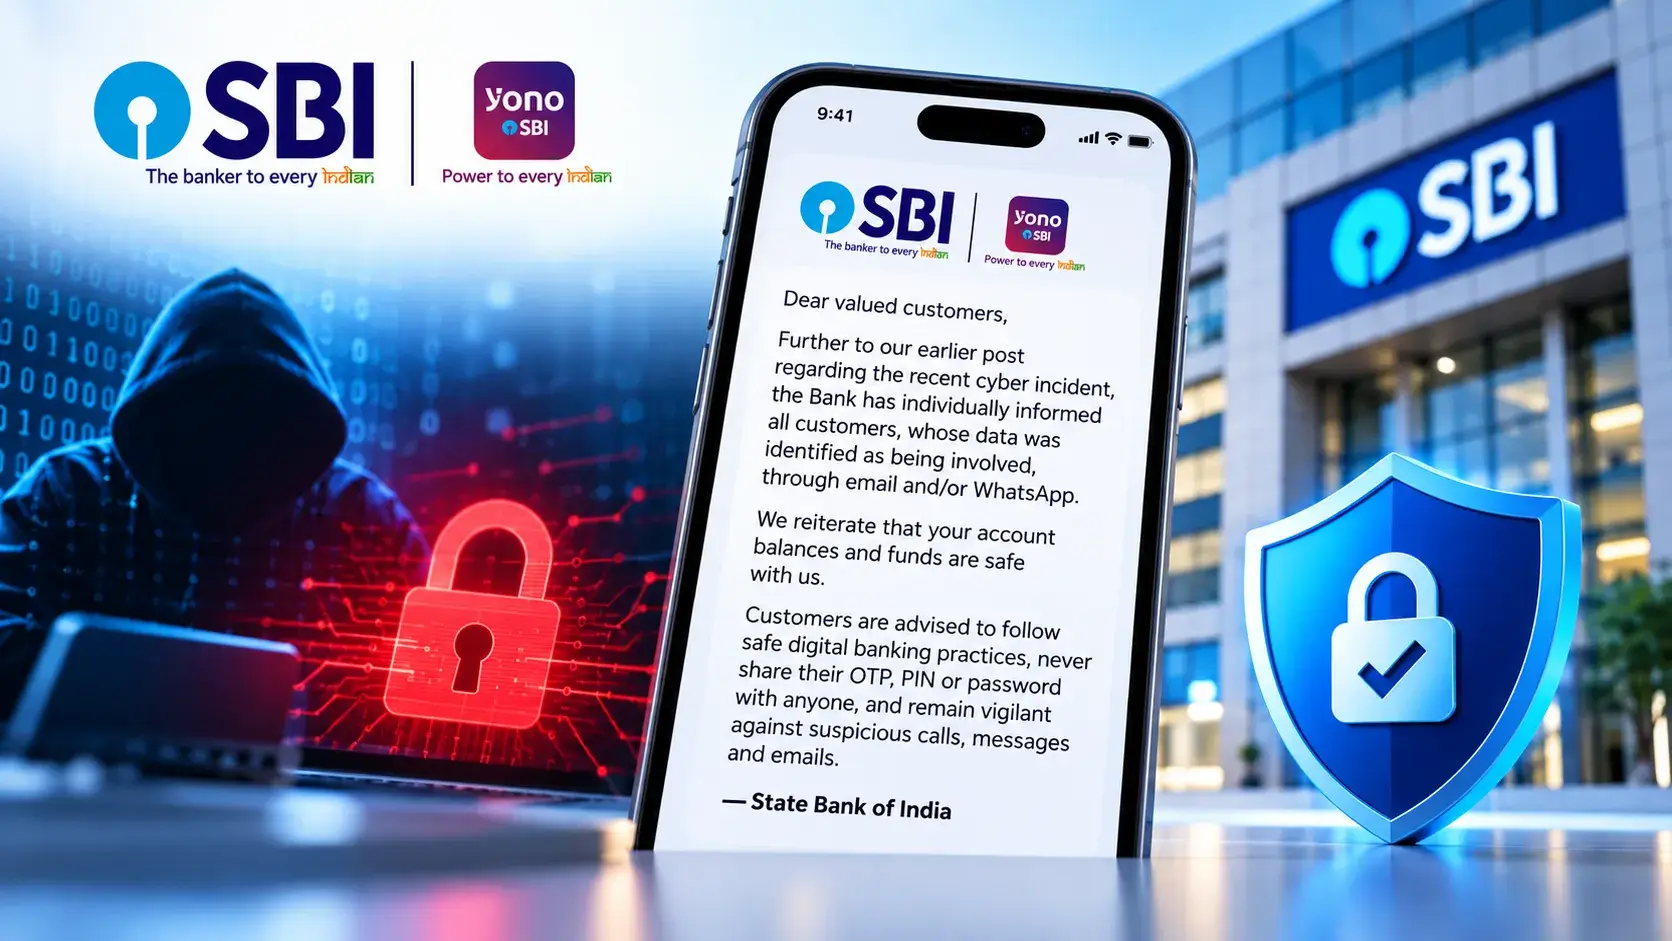
Hindiston Davlat Banki (SBI) yaqinda sodir bo'lgan kiberxavfsizlik hodisasi natijasida ma'lumotlari ta'sirlangan mijozlarni alohida xabardor qildi.
Mijozlar xavfsizligiga qaratilgan yangilanishda bank ta'sirlangan shaxslar bilan elektron pochta va/yoki WhatsApp orqali bog'langanini tasdiqladi. Ular mijozlarga hisob balanslari va mablag'lari xavfsiz ekanligini ta'kidladilar.
Ushbu e'lon hodisa haqida avvalgi xabarnomadan keyin e'lon qilindi. Biroq, xabarnomada buzilish qanday sodir bo'lgani, ta'sirlangan tizimlar, qancha mijoz jalb qilingani yoki qaysi turdagi ma'lumotlar buzilgani tushuntirilmagan. Ushbu kamchiliklar hodisaning ko'lami va texnik oqibatlarini mustaqil baholashga to'sqinlik qiladi.
Yangilanishga ko'ra, SBI ma'lumotlari buzilgan deb aniqlangan mijozlarga alohida xabarnomalarni yuborishni yakunladi.
Garchi matn mijoz ma'lumotlari ta'sirlanganini tasdiqlasa-da, hujumchilar ushbu ma'lumotlarga kirganmi, nusxa ko'chirganmi, e'lon qilganmi yoki boshqa tarzda suiiste'mol qilganmi — bu aniq emas. Ushbu farq e'lonni talqin qilishda muhim: ma'lumotlar jalb qilingani haqidagi xabarnoma avtomatik ravishda ommaviy ochiq ma'lumotlar bazasi yoki o'g'irlangan yozuvlarning aniq hajmini anglatmaydi; xabarnoma bularning hech birini tasdiqlamaydi.
SBI hech qanday tahdid aktorini nomlamadi, hodisani ransomware (tovon dasturi) bilan bog'lamadi yoki dastlabki kirish nuqtasi sifatida zaiflik, buzilgan hisob ma'lumotlari yoki uchinchi tomon xizmati aniqlanmadi. Bayonotda shuningdek, buzilish ko'rsatkichlari, sud-tibbiy xulosalar yoki tuzatish muddatlari haqida ham ma'lumot berilmagan.
Bank shunday dedi: "Biz sizning hisob balanslaringiz va mablag'laringiz bizda xavfsiz ekanligini takrorlaymiz." Bu mijoz mablag'lari haqida kafolat; biroq, ta'sirlangan ma'lumotlarning maxfiyligi yoki jalb qilingan tizimlar haqida aniqroq ma'lumot bermaydi.
Yangilanishda hodisa sanasi yoki bank faoliyatni qanday aniqlagani haqida ma'lumot yo'q. Shuningdek, tergov hali ham davom etayotgani yoki yo'qligi ham aniq emas. Natijada, faqat xabarnomaning o'zi hodisani batafsil qayta tiklash yoki cheklash (containment) haqida xulosa chiqarish uchun yetarli emas.
SBI mijozlarga xavfsiz raqamli bank amaliyotlariga rioya qilishni, masalan, OTP, PIN yoki parolni ulashmaslikni va shubhali qo'ng'iroqlar, xabarlar va elektron pochta xabarlariga hushyor bo'lishni tavsiya qildi.
Xulosa qilib aytganda, tasdiqlangan yangilik cheklangan: SBI aniqlangan ta'sirlangan mijozlar bilan bog'langanini va hisob balanslari hamda mablag'lar xavfsiz ekanligini ta'kidlaydi. Biroq, mijozlar yangilanishi texnik sabab, ta'sirlangan ma'lumot maydonlari, hodisa ko'lami yoki tergov natijalarini oshkor qilmaydi, bu esa muhim ma'lumotlarning ommaviy e'lon qilinishini imkonsiz qoldiradi.
The State Bank of India (SBI) has individually notified customers whose data was involved in a recent cybersecurity incident.
In an update focused on customer safety, thebank confirmed it contacted affected individualsvia email and/or WhatsApp. They reassured customers that their account balances and funds are safe.
This announcement follows an earlier communication about the incident. However, the notice does not explain how the breach occurred, identify the affected systems, disclose how many customers are involved, or specify which types of information were compromised. These omissions hinder an independent assessment of the incident’s scope and technical implications.
According to the update, SBI has completed individual notifications to customers whose data was identified as compromised.
While the wording confirms that customer information was affected, it does not clarify whether attackers accessed, copied, published, or otherwise misused that information.
This distinction matters for interpreting the announcement: a notification of data involvement does not automatically imply a publicly exposed database or aspecific volume of stolen records; the notice establishes neither.
SBI did not name any threat actor, attribute the incident to ransomware, or identify a vulnerability, compromised credential, or third-party service as the initial access point. The statement also provided no indicators of compromise, forensic findings, or remediation timeline.
The bank stated, “We reiterate that your account balances and funds are safe with us.” This is an assurance about customer money; however, it provides no more specific information about the confidentiality of the affected data or the systems involved.
The update does not mention the incident’s date or explain how the bank detected the activity. It also does not clarify whether the investigation is still ongoing. As a result, the notice alone cannot support a detailed reconstruction of the incident or conclusions about containment.
SBI advised customers to follow safe digital banking practices, such as not sharing an OTP, PIN, or password, and to stay alert for suspicious calls, messages, and emails.
In summary, the confirmed development is limited: SBI states it has contacted identified affected customers and maintains that account balances and funds are secure. However, the customer update does not disclose the technical cause, affected data fields, incident scale, or investigative findings, leaving critical information unavailable for public release.
Stops Cyber threats before impact with 21 min faster MTTR. Integrate ANYRUN’s Sandbox in your SOC.